Whitelisting Domains
Global Settings 'Domain List' Now Available For Enhanced Security
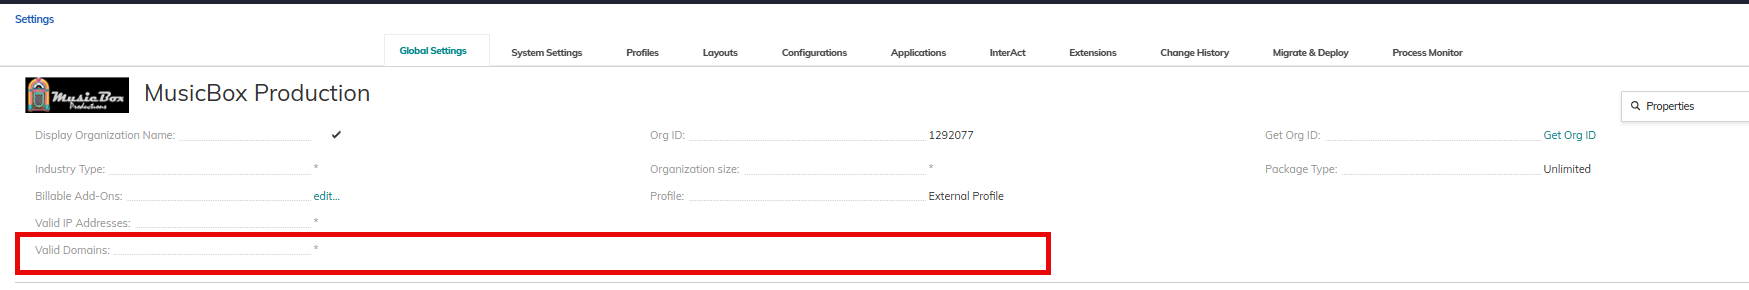
To strengthen the security framework for your organization, a new global setting has been introduced that enables domain white listing. This setting allows administrators to specify a list of approved domains that the organization is permitted to interact with.
When the white list is not configured, the system will, by default, allow access to all domains. However, once a white list is defined, only the domains explicitly included in the list will be accessible(including your own). All other domains will be automatically restricted, thereby reducing exposure to untrusted or potentially malicious endpoints.
This feature provides an additional layer of control over domain-level access and is especially useful in environments where compliance, data security, and access governance are critical. Administrators can configure the white list through the global settings interface to ensure that all domain communications adhere to organizational policies.
Relevant domains would need to include https:// (e.g. https://planview.com) and be separated by comma.
The feature supports only browser based requests (UI or API browser based) that contain the Origin attribute.
REST APIs from service/servers that do not contain the Origin attribute are not supported.